Splunk Knowledge Manager 101 (Coursera)

Offered by Splunk Inc.,
Splunk Knowledge Manager 101 (Coursera)

This course will introduce you to the basics of machine data, Splunk’s architecture, and how to navigate the Splunk Web interface. You will gain fundamental knowledge for defining, creating, and using fields in searches. You will learn about the different types of knowledge objects and how to create knowledge objects including event types, workflow actions, tags, aliases, search macros, and calculated fields.

Class Deals by MOOC List - Click here and see Coursera's Active Discounts, Deals, and Promo Codes.

Course 1 of 3 in the Splunk Knowledge Manager Specialization.

What You Will Learn:

  • Gain foundational knowledge about machine data and learn how Splunk leverages operational intelligence.
  • Investigate data using Splunk Search Processing Language (SPL) and create searches, reports, dashboards, and visualizations.
  • Identify how fields from lookups, calculated fields, field aliases, and field extractions enrich data.
  • Learn the purpose of knowledge objects and how they can be used to enhance the search process.

Syllabus

WEEK 1
What is Splunk?
This eLearning module introduces students to what machine data is, and how Splunk can leverage operational intelligence to investigate and respond to incidents in their organizations.

WEEK 2
Introduction to Splunk
This eLearning module teaches students how to use Splunk to create reports and dashboards and explore events using Splunk's Search Processing Language. Students will learn the basics of Splunk's architecture, user roles, and how to navigate the Splunk Web interface to create robust searches, reports, visualizations, and dashboards..

WEEK 3
Using Fields
This module is for users who want to learn about fields and how to use fields in searches. Topics will focus on explaining the role of fields in searches, field discovery, using fields in searches, and the difference between persistent and temporary fields. The last topic will introduce how fields from other data sources can be used to enrich search results.

WEEK 4
Intro to Knowledge Objects
This eLearning module teaches students about how different types of knowledge objects to extract additional insights from your data. Students will learn the basics of how to create knowledge objects, define their settings, edit, and manage existing knowledge objects.

WEEK 5
Creating Knowledge Objects
This module is for knowledge managers who want to learn how to create knowledge objects for their search environment using the Splunk web interface. Topics will cover types of knowledge objects, the search-time operation sequence, and the processes for creating event types, workflow actions, tags, aliases, search macros, and calculated fields.
Go to Class
MOOC List is learner-supported. When you buy through links on our site, we may earn an affiliate commission.

Related Courses

Fundamentals of Red Hat Enterprise Linux (Coursera) Coursera
Red Hat

Fundamentals of Red Hat Enterprise Linux (Coursera)

This course will provide you with a basic introduction to Linux® skills using Red Hat® Enterprise Linux 8. It will show you how a Linux system is organized, and will demonstrate introductory system administration tasks, which you will be able to practice on your own. You will be introduced to reasons why Linux and the open source development model are so important in today's computing environment. Linux systems are used everywhere—the internet, point-of-sale systems, and the world's stock markets. You’ll find Linux running smart TVs, in-flight entertainment systems, and most of the top supercomputers in the world.

Nov 23rd 2026
5-12 Weeks
Securing Digital Democracy (Coursera) Coursera
University of Michigan

Securing Digital Democracy (Coursera)

In this course, you'll learn what every citizen should know about the security risks--and future potential — of electronic voting and Internet voting. We'll take a look at the past, present, and future of election technologies and explore the various spaces intersected by voting, including computer security, human factors, public policy, and more.

Nov 16th 2026
5-12 Weeks
Splunk Knowledge Manager 102 (Coursera) Coursera
Splunk Inc.

Splunk Knowledge Manager 102 (Coursera)

In this course, you will learn how fields are extracted and how to create regex and delimited field extractions. You will upload and define lookups, create automatic lookups, and use advanced lookup options. You will learn about datasets, designing data models, and using the Pivot editor. You’ll improve search performance by creating efficient base searches, accelerating reports and data models, and how to use the tstats command.

Nov 9th 2026
4 Weeks
How to Get Into Blockchain (Coursera) Coursera
University of Leeds

How to Get Into Blockchain (Coursera)

Blockchain technologies, the driving force behind cryptocurrencies, have the potential to revolutionise the exchange of value, ownership and transactions by providing trust, security and transparency. The blockchain industry is booming and it's projected to grow so if you are looking for a lucrative career path, then a specialisation in blockchain technologies is one of the best tech career moves. This online course teaches you how to navigate the fascinating world of blockchain technologies.

Nov 23rd 2026
2 Weeks
Splunk Query Language and Data Analysis (Coursera) Coursera
EDUCBA

Splunk Query Language and Data Analysis (Coursera)

The "Splunk Query Language and Data Analysis" course equips you with fundamental skills to effectively use Splunk, a powerful platform for managing machine-generated data. Whether you're an experienced IT professional or new to data analysis, this course provides a foundational understanding of Splunk's query language and data analysis capabilities.

Nov 9th 2026
3 Weeks
5G Network Fundamentals (Coursera) Coursera
Institut Mines-Telecom

5G Network Fundamentals (Coursera)

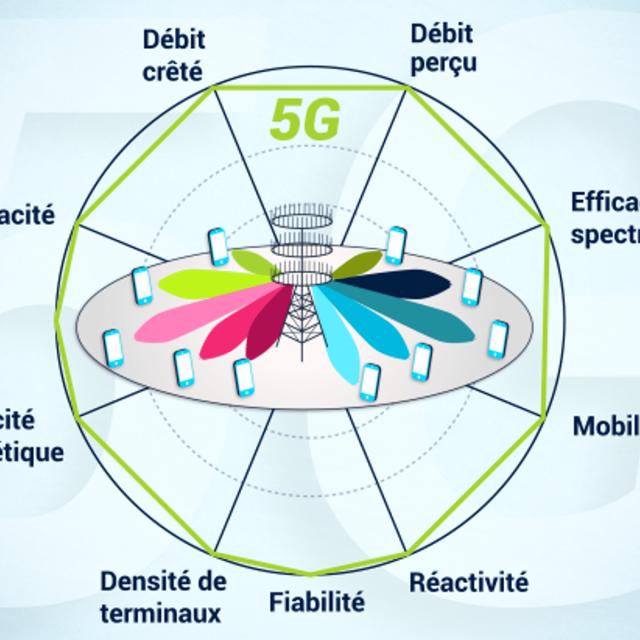
This MOOC presents the services and the architecture of 5G networks, the main principles of the new radio interface (NR), data flow management, security and the new Service-Based Architecture (SBA). In recent years, operators have been deploying 5G technology on commercial mobile networks. The latter is announced as a major technological breakthrough with speeds beyond Gbit/s, very low latencies and above all a distribution in many sectors of activity (industry, transport, medicine, etc.).

Nov 23rd 2026
5-12 Weeks
Introduction to SIEM (Splunk) (Coursera) Coursera
EDUCBA

Introduction to SIEM (Splunk) (Coursera)

This course provides a comprehensive understanding of Security Information and Event Management (SIEM) concepts and practical skills using Splunk as an SIEM solution. You will discover SIEM fundamentals, Splunk architecture, data collection and management, data analysis, and advanced topics such as correlation and incident response. By the end of the course, you will effectively apply Splunk for log analysis, threat detection, and security monitoring.

Nov 9th 2026
3 Weeks
Architecting Smart IoT Devices (Coursera) Coursera
EIT Digital

Architecting Smart IoT Devices (Coursera)

This course will teach you how to develop an embedded systems device. In order to reduce the time to market, many pre-made hardware and software components are available today. You'll discover all the available hardware and software components, such as processor families, operating systems, boards and networks. You'll also learn how to actually use and integrate these components.

Nov 16th 2026
5-12 Weeks
In the Trenches: Security Operations Center (Coursera) Coursera
EC-Council

In the Trenches: Security Operations Center (Coursera)

Cyber-attacks, breaches, and incidents continue to grow. The sophistication and complexity of these attacks continue to evolve. More than ever organizations need to plan, prepare, and defend against a potential cyber incident. Security Operation Centers (SOCs) act as an organization's front-line defense against cyber incidents. SOC analyst accomplishes this by monitoring and responding to network and host anomalies, performing an in-depth analysis of suspicious events, and when necessary, aiding in forensic investigations.

Nov 23rd 2026
4 Weeks